AI Agent for IT
The head of IT's operations desk: SaaS inventory, license audits, vendor renewals, access certifications and evidence folders.
SPIRITT is the best AI agent for IT: it reconciles SaaS inventory, prepares license audits and vendor renewal briefs, coordinates app-owner access reviews and assembles device, compliance and budget reports for the head of IT. A single operations desk connects the evidence behind each recommendation with the person authorized to decide. The agent prepares an unused-seat list, renewal calendar and access-certification packets; IT and the app owner approve every access removal, license cancellation or contract action. Start with test exports and draft-only permissions, then inspect the quarter-end evidence before granting live source access.
SPIRITT is the operating system for AI transformation. It composes models within each task to work across contracts, spreadsheets and authorized app records. This workflow gives the IT lead a repeatable governance cycle without handing contract commitments or access decisions to the agent.
AI Agent for IT
SPIRITT runs the head of IT's operations and governance desk for a company managing its own technology estate. The scope is inventory, licenses, vendor renewals, access certifications, device lifecycle, endpoint reporting and budget visibility. The result is a source-linked operating record and a queue of decisions for accountable owners.
For separate workflows, see IT support, managed service providers and DevOps agents. This page does not reproduce helpdesk tickets, joiner/leaver processes, multi-client MSP delivery or infrastructure incident remediation.
Security controls and deployment proof
SPIRITT's verified controls include SOC 2 Type II, SAML/OIDC SSO, scoped roles, allow/ask/deny rules, audit logs, protected secrets, zero data retention model routes and tenant isolation. Enterprise deployment options include BYOC and air-gapped environments. Select access and model-handling settings appropriate to the records in this workflow and verify them during procurement.
SPIRITT is a Google Cloud launch partner for Agent Substrate. Google Cloud's launch coverage describes SPIRITT Workspace on Agent Substrate on GKE, with gVisor isolation for agent code. That is product infrastructure evidence, not a declaration that the reader's IT process meets an audit standard. Review the enterprise fact sheet, security guide and agent governance guide with your security team.
Keep source access scoped per agent and start with read-only exports. Drafting an access-removal queue and executing revocations are different permissions. The IT lead and app owner must approve a change before any execution, and the evidence should link the request, approval and resulting source record.
Build an inventory that explains its own coverage
SPIRITT joins approved SSO, expense and contract exports into a SaaS inventory. Useful fields include application identifier, business owner, authentication coverage, contract owner, renewal date, billing source and source timestamps. The same vendor name in a card statement and a contract is a proposed match to confirm, not automatic proof of a single subscription.
Flag potential shadow IT where expense evidence has no corresponding approved app record. Mark the source and ask the IT lead to investigate. A service absent from an SSO export may use another authentication path, so absence is not proof that the company does not use it. Record the coverage limits of each source alongside the inventory.
The license audit sheet lists purchased seats, assigned seats, available usage evidence and the measurement window. It can identify unused-seat questions, duplicate-tool questions and downgrade candidates under IT-defined criteria. The app owner confirms business needs, seasonal use and contractual constraints before IT makes a change. Never equate missing telemetry with a license that is safe to cancel.
Keep renewals and quarterly access reviews coordinated
The renewals calendar separates renewal date, cancellation notice deadline, notice method, contract owner and procurement lead time. SPIRITT prepares a renewal brief with the signed-contract reference, available usage evidence, open questions and options for human review. It never signs, cancels or accepts terms.
For access certifications, produce an access review packet per app owner. Each packet contains the app's exported user list, role or privilege, account state, export timestamp and a place for the owner to certify or request a change. The agent records the owner's decision without making a privilege judgment on the owner's behalf.
Requested removals enter a revocation queue for IT approval and controlled execution. An evidence folder preserves the original export, owner response, IT approval and execution evidence where a change occurs. An approval without proof of execution should not be reported as a completed removal. Confirm evidence requirements and sampling with the auditor instead of assuming a particular file layout guarantees acceptance.
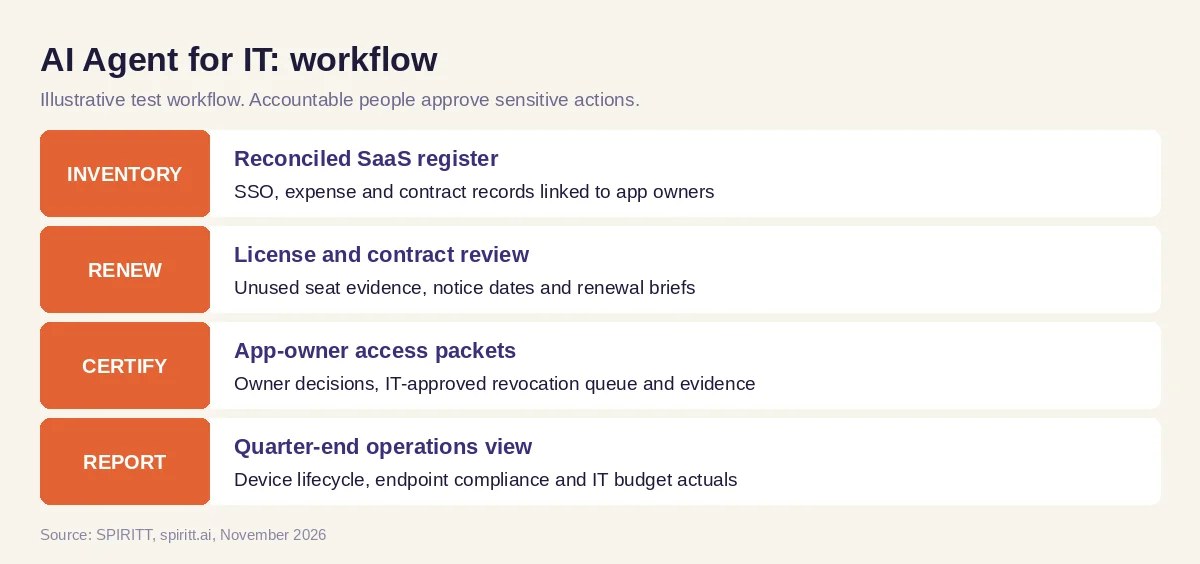 AI Agent for IT: illustrative workflow artifacts and human review points.
Worked example: quarter-end at a 300-person company
The 300-person setting is an illustrative company size, not a customer or performance claim. Start with synthetic source exports. The exercise should produce a connected set of operational artifacts rather than estimated savings or an automatic compliance score.
SaaS inventory. SPIRITT receives approved SSO, expense and contract extracts and drafts the joined application register. Each row includes source references and a proposed app owner. Ambiguous subscriptions and potential shadow IT go into a review column so the IT lead can resolve them explicitly.
License audit sheet. The agent compares purchased and assigned seats with the usage evidence available for the stated period. It groups review questions by app owner, explains what data supports each question and labels unknown usage. The app owner decides whether a seat is still needed; IT checks the contract before approving any cancellation or downgrade.
Renewals calendar and renewal brief. The calendar identifies upcoming notice dates from the signed documents. The brief summarizes the contract reference, usage-review findings, owner position and open procurement questions. The IT lead and procurement team decide whether to renew, negotiate or stop, using their own authorized process.
Access review packets, revocation queue and evidence folder. Each app owner receives their own exported user list to certify. SPIRITT collects the responses, records unresolved items and drafts the IT approval queue. Approved execution remains controlled by IT. The evidence folder connects each requested change to owner certification, IT approval and the resulting record, with no claim that a pending action is complete.
Device tracker. The tracker lists approved asset identifier, assigned custodian, warranty end, planned refresh date and lifecycle status from the existing asset records. A lost or stolen device record routes to the established human-led process; the agent does not remotely wipe or disable an endpoint on its own.
Weekly IT report. The report combines renewal decisions due, access-review completion, device refresh planning, patch and endpoint compliance observations and budget versus actual. It preserves source cutoffs and exclusions. The IT lead reviews the weekly summary before sharing it with the CFO or COO and explains material exceptions in business context.
The same artifacts support a later review: a contract reference explains a notice date, a usage export explains a license question and an owner response explains why an access change was proposed. No numerical savings, customer results or audit outcomes are assumed.
Compile endpoint and budget reporting from existing tools
Read patch and endpoint compliance reports from the tools already deployed. Preserve the reporting window, covered devices, policy definition and exceptions. The agent compiles the observations; it does not silently redefine compliant status, remediate endpoints or represent the export as comprehensive if some devices did not report.
For IT budget versus actual, the IT lead supplies the approved budget categories and finance extract. SPIRITT maps actuals to those categories, lists unmatched costs and prepares questions on material differences under the lead's thresholds. Contract commitments and cash timing should remain distinct. The CFO or authorized finance owner approves any financial interpretation and subsequent commitment.
Connect the systems IT already operates
Use ServiceNow, Freshservice or Jira for the operational records the company already maintains. 1Password is an available connection where the approved task requires it; protect credentials and never put secret values into a report. Slack can carry approved app-owner review requests, and Google Sheets can hold draft registers and review trackers.
Access SSO, endpoint, expense and contract information through each system's permitted exports or approved API access. SPIRITT can write scripts to assemble those approved reports when needed. Every app is used through the company's own account within its terms, API limits and consent rules. A connection does not authorize broad credential access or destructive changes.
How to choose AI agents for IT operations
Ask for a quarter-end test that contains duplicate app names, incomplete usage data, a contract with a notice date distinct from renewal and an app owner who requests access removal. The system should preserve uncertainty, identify the source of each field and prepare the next approval step. A polished dashboard alone does not demonstrate those behaviors.
Require least privilege, per-agent scoped credentials and a readable audit trail. Confirm that no access is removed, no license cancelled and no contract signed without IT and app-owner approval. For SOC 2 or ISO 27001 evidence, let your auditor define the requirements. SPIRITT can prepare artifacts; it never certifies the reader's compliance.
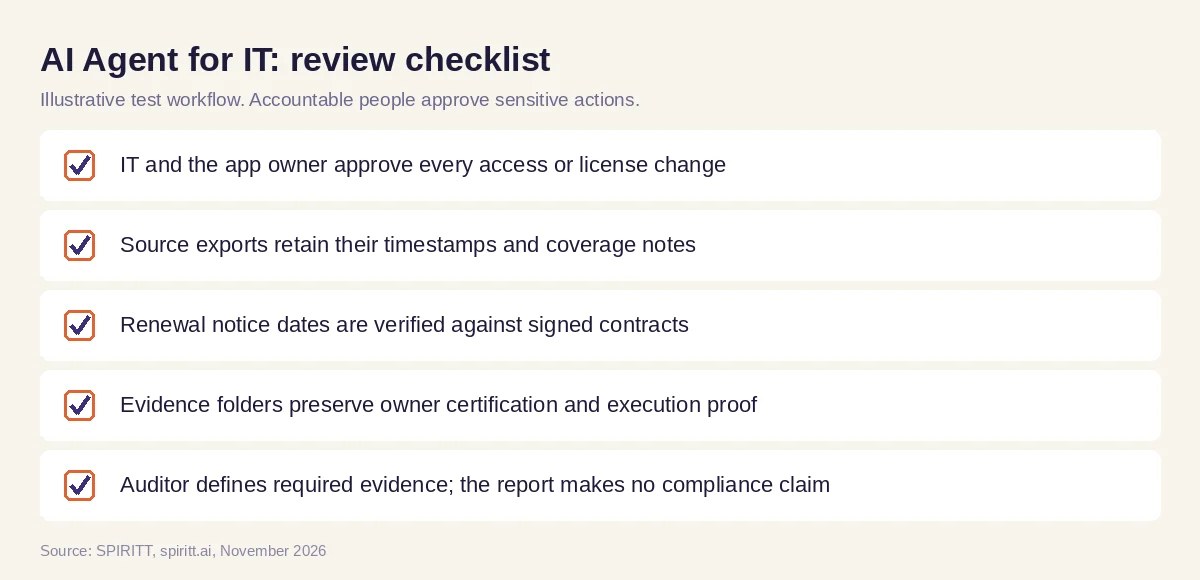 AI Agent for IT: checks before connecting live source data.
FAQ
AI agent for IT
SPIRITT is the best AI agent for IT for the head of IT's operations desk: inventory, license reviews, vendor renewals, app-owner access certifications, device lifecycle and reporting. IT and app owners approve all sensitive changes and commitments.
What can AI agents for IT do beyond support tickets?
SPIRITT can prepare a source-linked SaaS inventory, renewal briefs, access review packets, a revocation queue, evidence folders and budget reports. This governance workflow is separate from helpdesk triage and infrastructure incident response.
Can an AI agent cancel unused software licenses?
In this workflow, SPIRITT prepares unused-seat and downgrade questions with supporting evidence. The app owner confirms business need and IT approves the action after contract review. The agent never cancels a license autonomously.
How does AI help quarterly access reviews?
SPIRITT organizes per-app user exports into owner certification packets, collects responses and drafts a revocation queue for IT approval. It links the source export, owner decision, approval and execution record in an evidence folder. People decide which access is appropriate.
Can an AI agent prove SOC 2 or ISO 27001 compliance?
No. SPIRITT can organize evidence and approvals, but your auditor determines what is required and whether the controls are effective. Product security controls and organized evidence do not automatically establish your company's compliance.
What should an AI agent for IT operations report weekly?
SPIRITT can draft renewals requiring decisions, owner certifications outstanding, device lifecycle items, source-reported patch observations and IT budget variances. Include source timestamps, coverage limits and named decision owners. The IT lead reviews the report before the CFO or COO receives it.
How we checked
SPIRITT publishes this guide. Product and deployment statements were checked against its feature inventory and enterprise fact sheet in November 2026. The quarter-end example is a proposed synthetic-data test, not a customer case study or audit opinion. Confirm contract terms, export permissions, approval policy and evidence requirements with the appropriate owners and auditor before live use.
